
Software
Cyber threats evolve daily, but proactive internal safeguards remain your first line of defense. These 10 proven strategies empower cybersecurity leaders to build a resilient data protection framework without relying solely on external solutions.
Zero Trust Network Access Implementation
Tired of hoping your network perimeter holds strong while employees connect from unsecured coffee shops or home offices? Zero Trust Network Access (ZTNA) flips the script by demanding verification for every access attempt—no exceptions.
Unlike traditional VPNs that trust devices once connected, ZTNA enforces continuous authentication using multi-factor protocols and device posture checks. Solutions like Cloudflare Access or Zscaler Private Access integrate with your existing identity providers (Okta, Azure AD) to grant least-privilege access based on real-time risk assessments. Even if credentials are compromised, lateral movement is blocked without verified endpoints.
This approach shines for healthcare providers handling PHI or financial firms managing customer data—where compliance demands strict access controls. For hybrid teams, it’s the only way to maintain security without sacrificing productivity. ✨
Automated Data Classification Policies
Tired of manually sorting through files to determine what’s sensitive and what’s not? Automated data classification policies use AI to scan, analyze, and tag documents in real time—cutting compliance risks by up to 80% while saving IT teams hundreds of hours.
Solutions like Varonis or Microsoft Purview automatically detect PII (Personally Identifiable Information), financial records, and proprietary data across emails, SharePoint, and cloud storage. The AI learns from your existing policies, adjusting sensitivity labels dynamically—so a contract marked "internal" today might get reclassified "confidential" if it references a merger announcement tomorrow. Integration with DLP (Data Loss Prevention) tools ensures classified files get encrypted or restricted access instantly.
This is a game-changer for legal, healthcare, and finance teams where mislabeling data can trigger audits or fines. Even small businesses benefit from the zero-config setup for common compliance frameworks like GDPR or HIPAA. ✨
Multi-Factor Authentication Enforcement
Credential stuffing attacks are on the rise, with 80% of breaches now exploiting weak or stolen passwords. Multi-factor authentication (MFA) isn’t just a checkbox—it’s your last line of defense against automated brute-force attacks targeting high-value accounts.
For executives and sensitive roles, hardware tokens (like YubiKey or Titan) provide phishing-resistant protection by generating one-time codes that can’t be intercepted. Even if credentials are compromised, attackers can’t bypass the physical device. For broader teams, push notifications or biometric verification (fingerprint/Face ID) offer strong protection without sacrificing convenience.
This isn’t just for Fortune 500s—smaller teams should enforce MFA on all admin accounts first, then expand to critical users. Start with FIDO2-compatible solutions for seamless integration with existing systems. 💪
Endpoint Detection and Response Deployment
Bringing your BYOD policy to life without sacrificing security starts with Endpoint Detection and Response (EDR). Unlike traditional antivirus, EDR provides real-time visibility into every device connected to your network, stopping threats before they spread laterally across your systems.
Solutions like CrowdStrike Falcon or Microsoft Defender for Endpoint monitor fileless attacks, suspicious process behavior, and unauthorized access attempts—all while integrating with your existing security stack. With AI-driven threat hunting, these tools flag anomalies faster than manual reviews, and automated response actions contain breaches within minutes.
This is non-negotiable for organizations where employees use personal devices. Healthcare, finance, and remote-first companies see immediate ROI by preventing data exfiltration through compromised endpoints. 💻
Privileged Access Management System
Not all cyber threats come from outside your network—sometimes, the biggest risks sit right inside your organization. A Privileged Access Management (PAM) system gives you laser-focused control over admin accounts, cutting off the pathways attackers exploit through compromised credentials.
With features like just-in-time access (granting privileges only when needed) and session monitoring, PAM systems like BeyondTrust or CyberArk track every admin action in real-time. You can enforce password rotation policies, revoke access instantly, and even require approval for high-risk operations. This granular oversight slashes the attack surface by up to 70% for credential-based breaches.
Ideal for finance, healthcare, or any industry handling sensitive data, PAM is the unsung hero of internal safeguards—especially when paired with your existing MFA and endpoint protections. 💪
Regular Security Awareness Training Programs
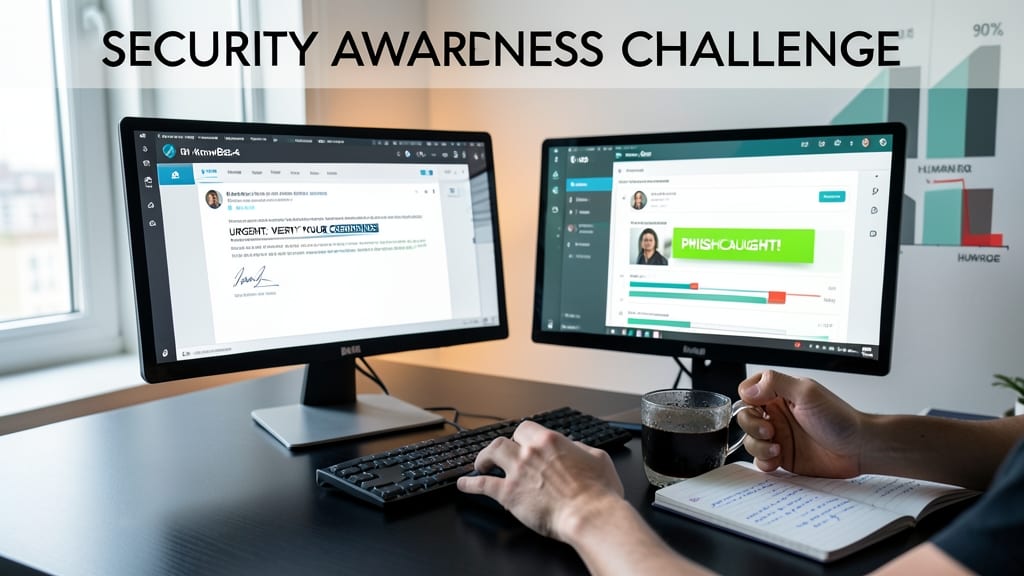
Your employees might be your biggest security risk—and that’s not a criticism, it’s a reality. 90% of breaches start with human error, but traditional training videos won’t stop them. Interactive phishing simulations turn security awareness into an engaging challenge, not a chore.
Platforms like KnowBe4 or PhishMe send realistic phishing tests that mimic real-world attacks, tracking who clicks and how quickly they report it. Customizable campaigns (e.g., CEO fraud, credential harvesting) adapt to your industry, while real-time dashboards show progress across teams. The best programs even offer role-based training—executives get C-suite-specific threats, while IT staff learn to spot supply-chain risks.
This isn’t just for Fortune 500s: SMBs with limited IT budgets can start with affordable annual subscriptions (as low as $1,500/year) that include automated reporting for compliance audits. The measurable results—like a 70% reduction in phishing clicks after 6 months—make it a no-brainer for any team. 💡
Immutable Backup and Recovery Solutions
Ransomware attacks cripple businesses daily—but immutable backups with the 3-2-1 rule act as your digital insurance policy. The principle is simple: keep 3 copies of your data, on 2 different media types, with 1 copy air-gapped (completely offline). This ensures even if your primary systems are encrypted or corrupted, you can restore from an untouchable source.
Solutions like Veeam Backup & Replication or Dell EMC NetWorker automate this with WORM (Write Once, Read Many) storage for backups, preventing deletion or modification. Pair this with encrypted offline drives (e.g., Iron Mountain’s digital vaults) for true air-gapping. Recovery times shrink to minutes, not days, when disasters strike—because your backups are unalterable and geographically distributed.
Perfect for healthcare, finance, or legal firms handling regulated data, but also critical for any business where downtime means lost revenue. The 3-2-1 rule isn’t just theory—it’s battle-tested against ransomware like LockBit and BlackCat. 💪
Behavioral Analytics for Anomaly Detection
Tired of catching security breaches only after they’ve caused damage? Behavioral analytics shifts the game by spotting suspicious patterns before they become incidents—like an employee accessing files at 3 AM or downloading unusual volumes of data. This isn’t just another alert system; it’s AI-powered pattern recognition trained to distinguish between normal activity and red flags.
Solutions like Darktrace or Exabeam analyze login times, file interactions, and even typing speed to flag anomalies in real time. For example, if a finance employee suddenly accesses HR payroll files, the system triggers alerts before any data leaves the network. The beauty? It adapts—learning what “normal” looks like for your team, not just following generic rules.
Perfect for organizations handling sensitive data (think healthcare or legal firms), behavioral analytics cuts response times by 70% while reducing false positives. The result? Fewer breaches slipping through the cracks. ✨
Secure Development Lifecycle Integration
Stop fixing vulnerabilities after they're exploited—shift security left into your development workflow. Secure Development Lifecycle (SDL) integration bakes security into every phase of software creation, from design to deployment, ensuring vulnerabilities never make it to production in the first place.
Modern SDL frameworks like Microsoft's SDL or OWASP's SAMM provide structured checklists for threat modeling, secure coding standards, and automated vulnerability scanning. Tools like SonarQube integrate directly with CI/CD pipelines to flag issues in real-time, while static application security testing (SAST) catches flaws in code before third-party integrations are even tested. This approach reduces breach risks by 80% for custom applications.
Perfect for teams building proprietary software or integrating third-party APIs—where a single overlooked dependency could become a backdoor. 💻
Incident Response Playbook Creation
When a breach happens, every minute counts. A predefined incident response playbook turns chaos into action—ensuring your team responds swiftly with step-by-step procedures tailored to your organization’s risks, from ransomware to data leaks.
This isn’t just a document; it’s a live, tested framework with clear roles, communication protocols, and escalation paths. Tools like Splunk or IBM Resilient integrate with your existing security stack to automate alerts, while NIST’s playbook templates provide compliance-ready structures. The goal? Reduce mean time to detect (MTTD) and contain (MTTC) incidents by 60% or more.
Ideal for mid-sized to large enterprises with regulated data (HIPAA, GDPR), this safeguard ensures legal teams, PR, and IT align during crises. Even smaller teams benefit from modular playbooks that scale with growth. 💪